Security
Testing
Find weaknesses, prove realistic attack paths and understand the consequences. Web, API, infrastructure, cloud, AI and adversarial testing.
Independent security expertise
From penetration testing and AI application security to SOC modernisation and detection engineering. We help you build effective security and test whether it actually works.
Practical engineering. Evidence-led testing. Clear outcomes.
What we do
Whether you need an independent penetration test or help improving how security operates, start with the outcome you're trying to achieve.
Find weaknesses, prove realistic attack paths and understand the consequences. Web, API, infrastructure, cloud, AI and adversarial testing.
Plan, build, mature and validate your security capability. Security architecture, SOC improvement, detection engineering and practical advisory.
Offensive security
From conventional penetration tests to AI and adversarial assessments, we test the weaknesses and attack paths that matter. Not sure what to buy? Use Find Your Test.
Manual authenticated testing, APIs, access control and business logic — not scanner output dressed up as a report.
Scope it → 02External and internal networks, Active Directory, segmentation, privilege escalation and the infrastructure behind the asset register.
Scope it → 03AWS, Azure and GCP exposure, identity, configuration, trust relationships and routes to higher privilege.
Scope it → 04Authentication, authorisation, object access, integrations and the business logic sitting behind your API surface.
Scope it → 05Agents, RAG, MCP, tool permissions, prompt injection, identity and whether trust boundaries actually hold.
Explore AI testing → 06Objective-led testing against people, process and technology to determine whether prevention, detection and response work together.
Scope it →Security operations & engineering
Security capability is more than tools and dashboards. We help organisations design, implement and improve the people, processes and engineering that make security effective.
Focused consultancy and delivery, scoped around what needs to change — not an open-ended transformation programme.
Security architecture, capability assessments, priorities and practical roadmaps.
Security controls, detection content, engineering workflows and automation.
SOC processes, vulnerability management, detection coverage and operational effectiveness.
Validate that controls, detections and operational processes deliver the intended outcomes.
Beyond the pentest
A penetration test is a point in time. Your environment, threats and attacker capabilities don't stand still.
SMARTSEC can extend traditional testing into ongoing adversarial assurance — identifying the paths that matter, validating whether your controls stop them, and re-testing them when your environment or the threat changes.
What continuous validation means
Already testing continuously? Good.
SMARTSEC doesn't require you to replace the tools or testing capability you already have. We can work with evidence from your internal security team, existing validation platforms and security tooling alongside independent testing performed by us.
The objective isn't to generate more findings. It's to determine whether credible adversaries can achieve outcomes that matter — and independently demonstrate where your controls stop them.
The SMARTSEC client platform
Continuous assurance needs more than a final PDF. Our client platform gives you one place to access published findings, track remediation, review reports and see the status of your assessments.
Findings become available as they are published during an engagement — not an unsupported promise of instantaneous automated detection.
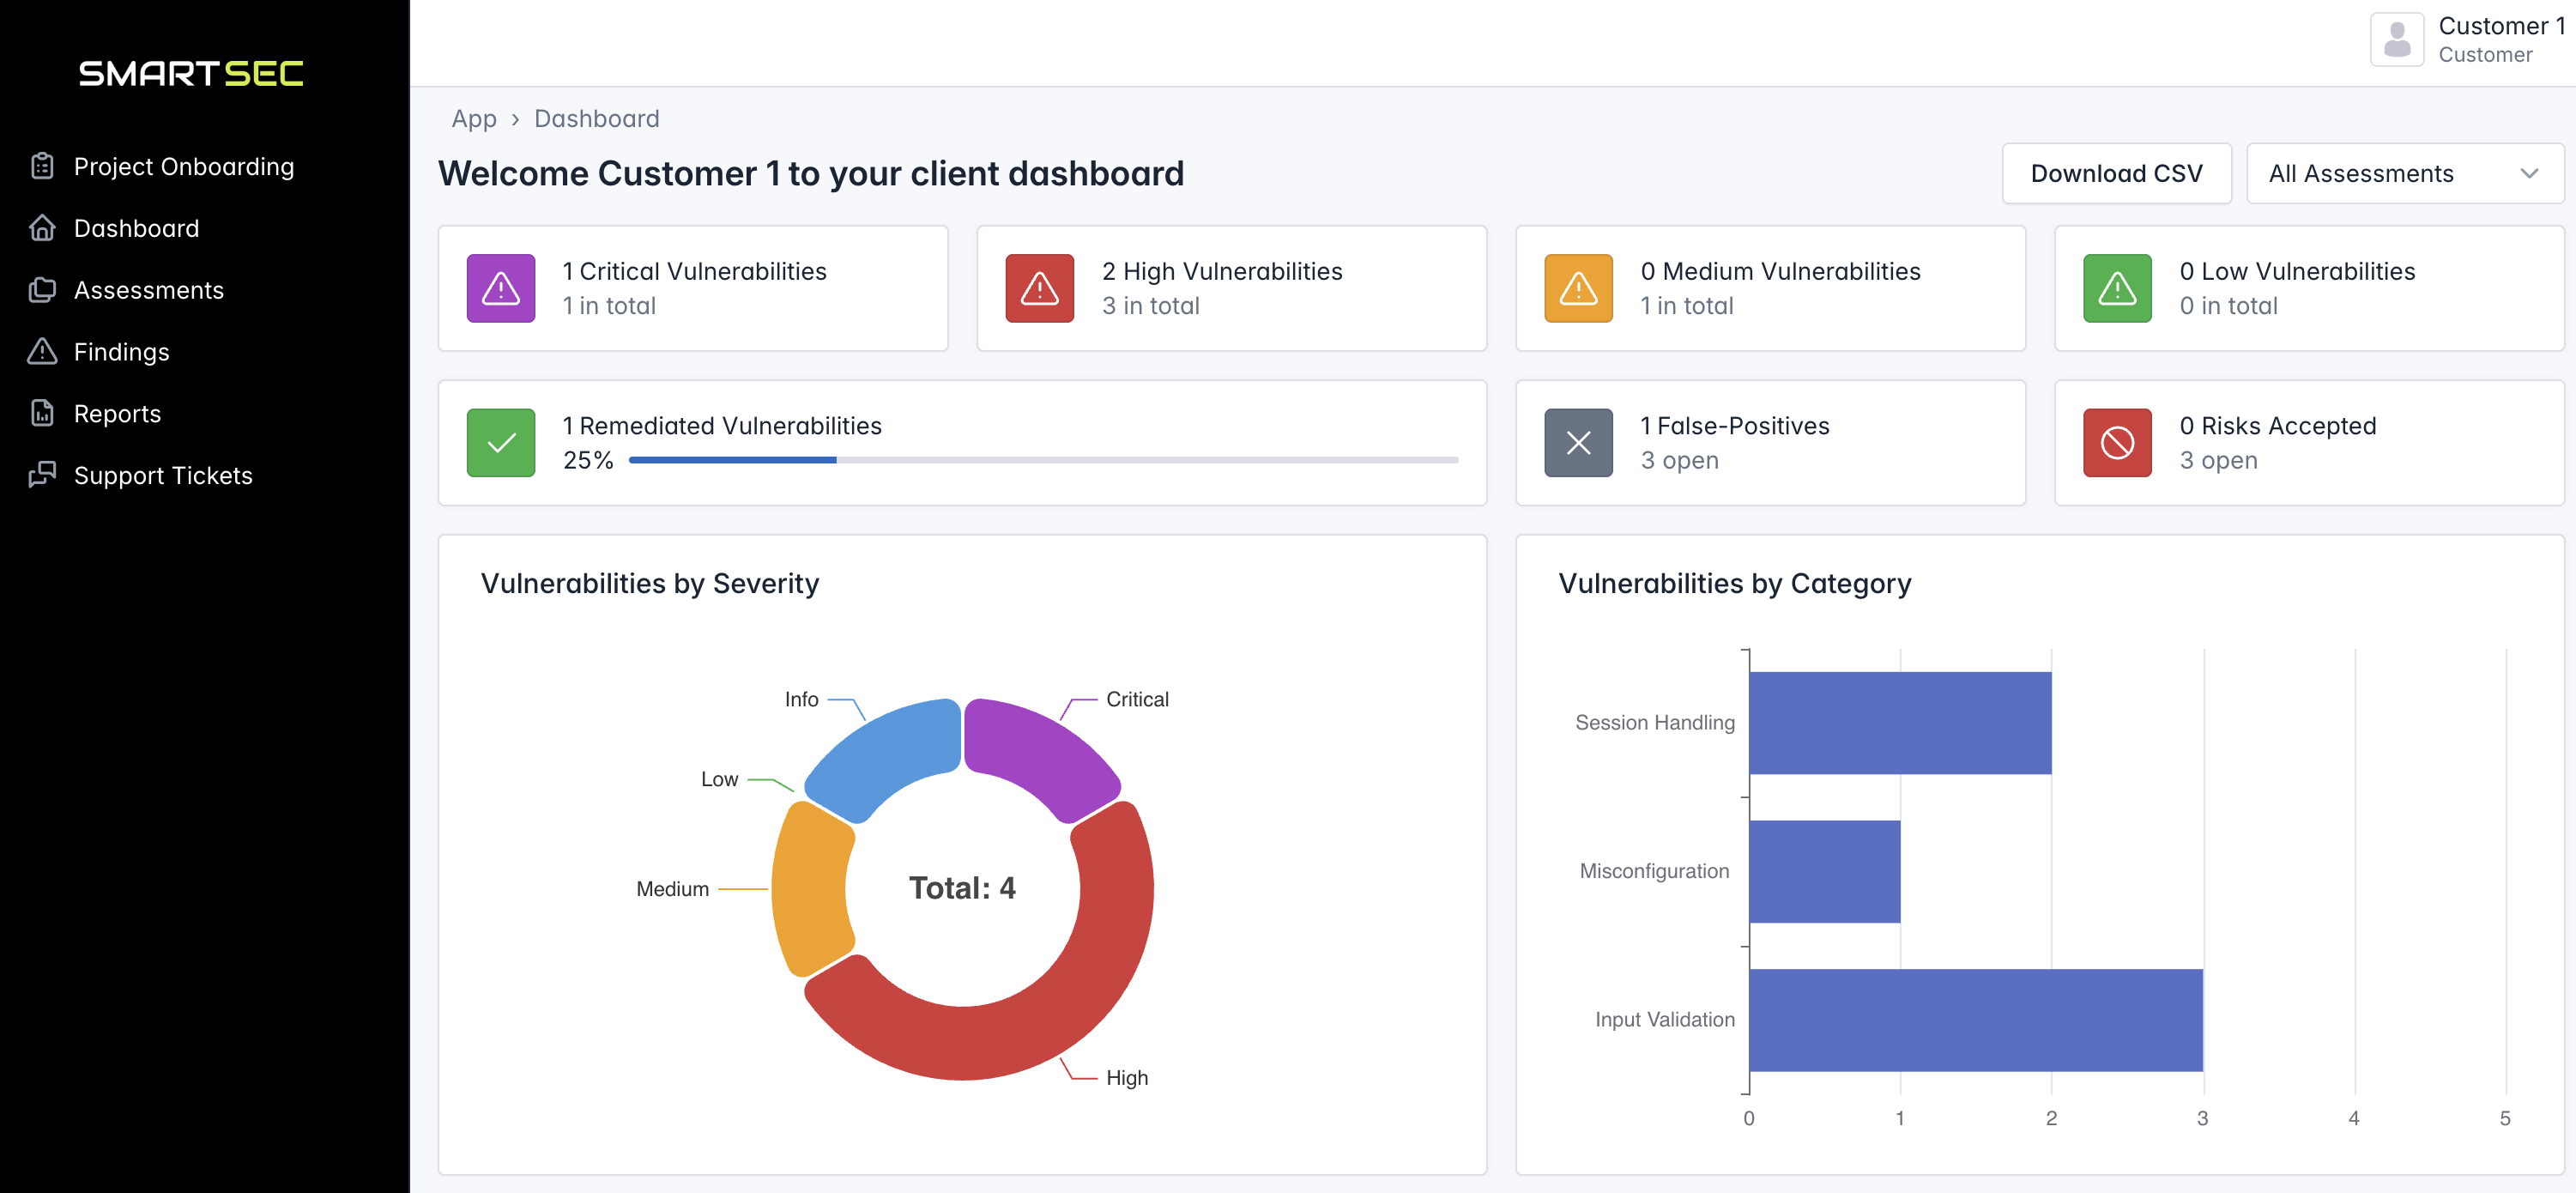
See vulnerability severity, categories and remediation progress from your customer dashboard. Understand what is open and what needs attention.
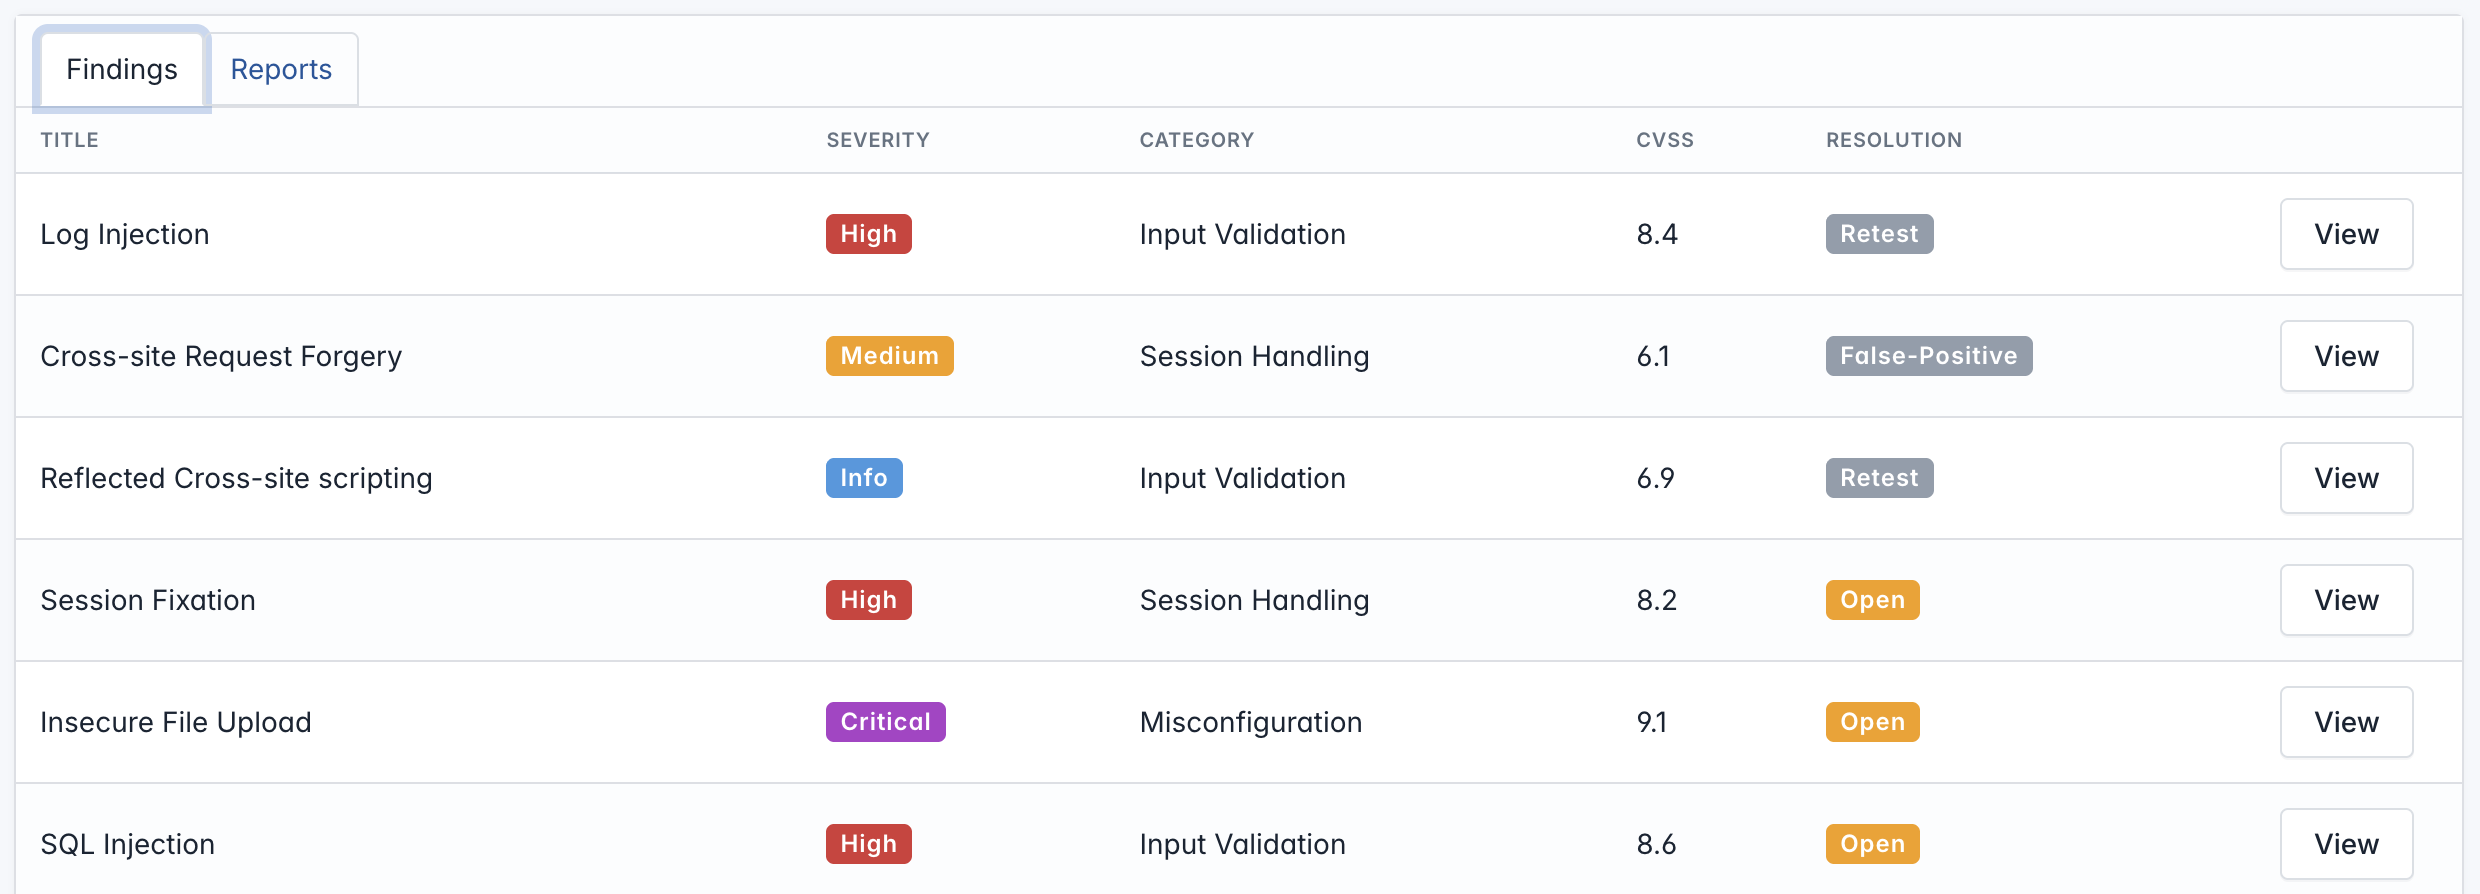
Review published findings, severities, CVSS scores and statuses without hunting through email threads.
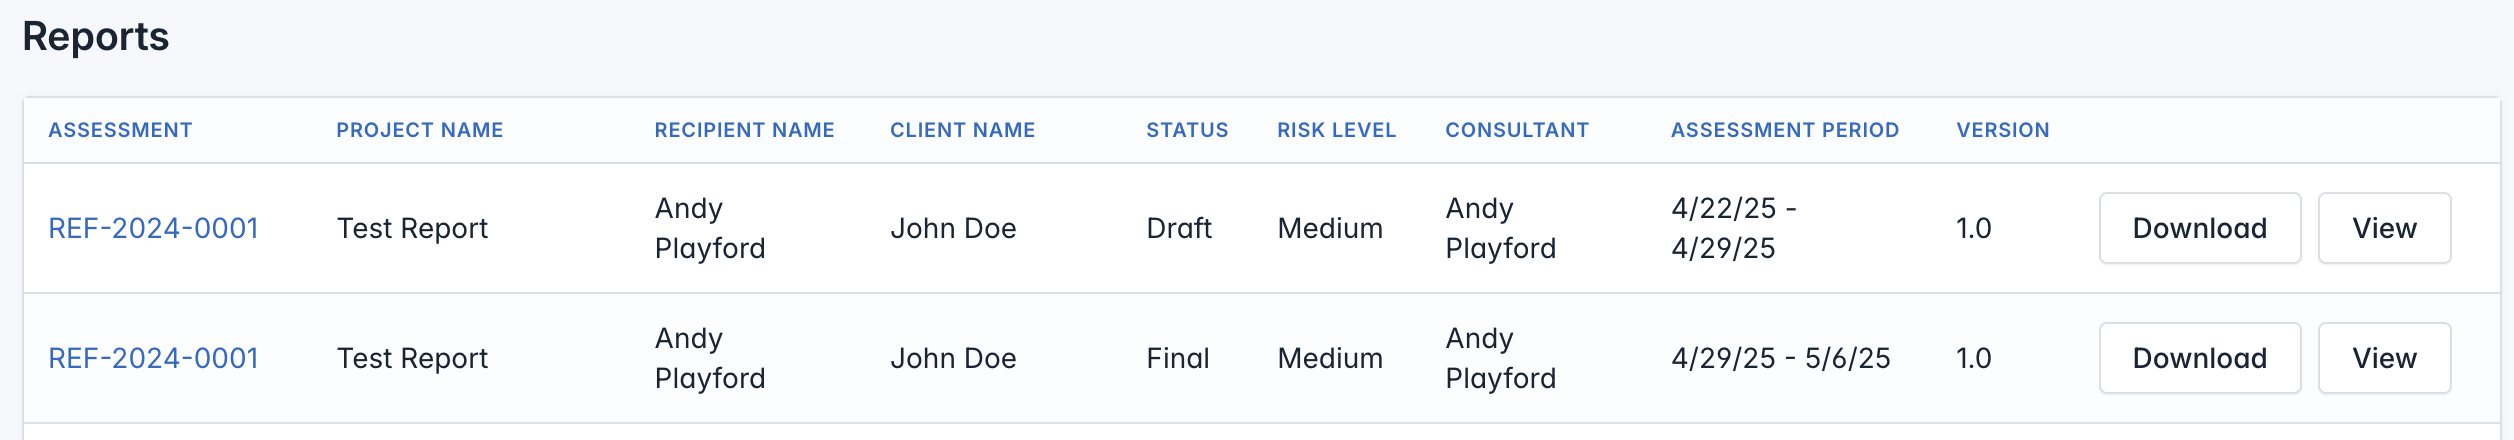
Access assessment reports and their versions from a central location, with clear project and reporting details.
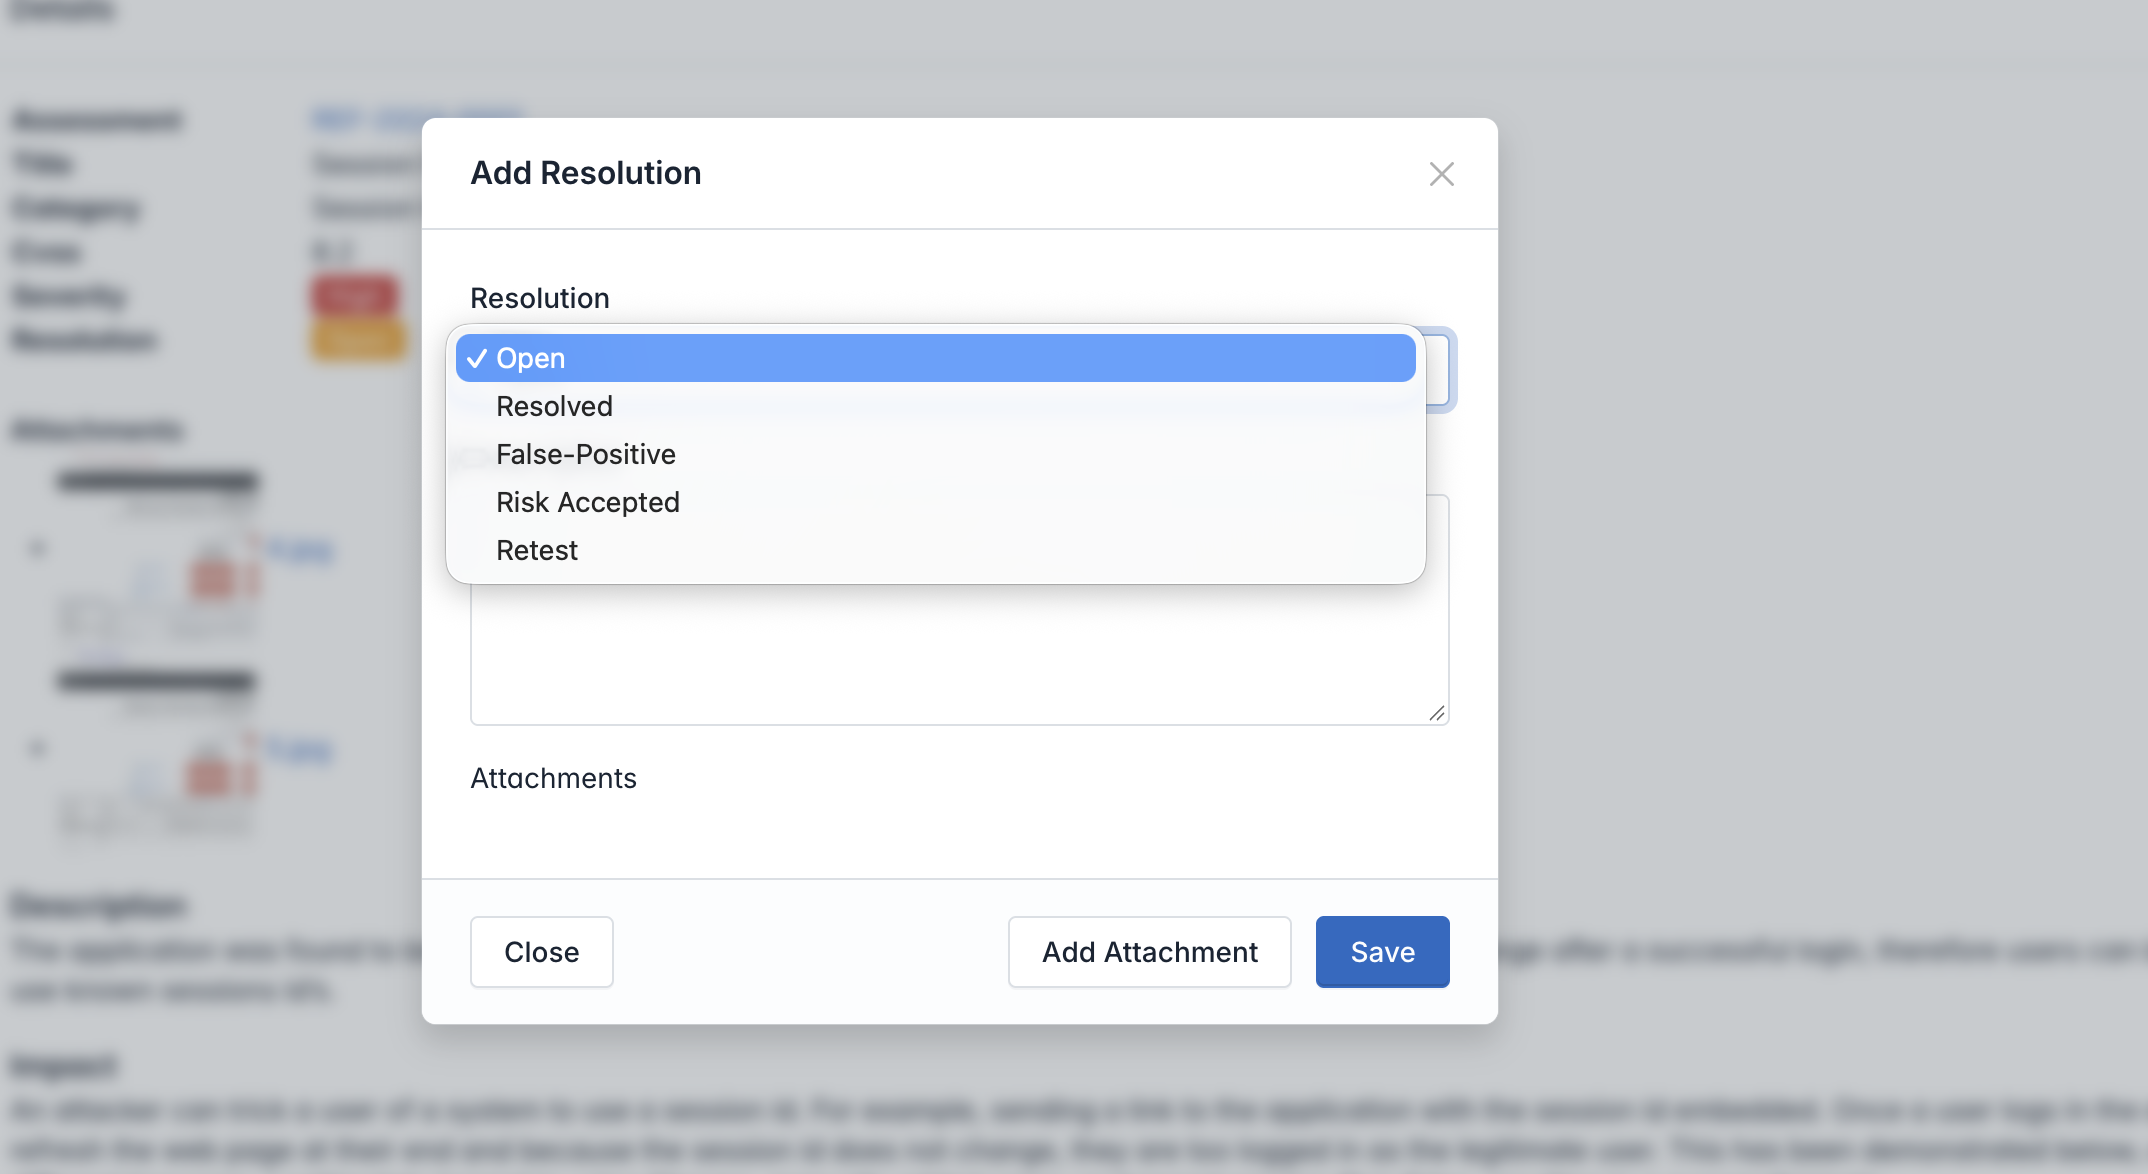
Update finding status, add supporting notes and attachments, and flag items for retesting. Maintain a visible record of the remediation process.
Get a clear route from discovery to remediation and independent revalidation.
Independent assurance
Threat-led testing and independent assurance for organisations operating in regulated or high-consequence environments.
Attack-path analysis
Individual vulnerabilities still matter. But the bigger question is what they allow an attacker to do next. Where findings, identities and trust relationships connect, we show the path, the controls encountered and the potential consequence.
Example attack path
Method
Automation expands coverage. Senior testers provide the judgement: business logic, unusual attack chains, trust relationships, exploitation decisions and the evidence required to support an assurance conclusion.
Define assets, objectives, rules of engagement, critical systems and the outcomes that matter.
Automated coverage and senior human testing across the authorised attack surface.
Determine whether individual observations combine into credible attack paths.
Test meaningful paths, record controls encountered and establish what an attacker could actually achieve.
Technical findings for engineers, attack-path evidence for security teams and consequence-focused assurance for decision makers.
After remediation, prove that the path is closed rather than assuming the individual finding fixed the problem.
Contact
Or tell us the outcome you're worried about and we'll help determine how to test it.
Let's talk
Tell us what you are building, protecting or trying to improve. We’ll help identify a sensible next step.
Email SMARTSEC →